The Lumora Security Brief | UAE Edition | July 2026
Welcome back to our latest issue of The Lumora Security Brief | UAE Edition
This month, security researchers watched an AI run a complete ransomware attack on its own. No human at the keyboard. It broke in, stole credentials, spread, and encrypted the data, fixing its own mistakes in under a minute.
That was July in one story. Attacks are getting faster and cheaper to run, and AI is the cause with the UAE squarely in the firing line. This month's edition dives into how this was possible, the fixes that can prevent future incursions, and some marquee cybersecurity events coming very soon in the months ahead.
July Month's Threat Updates: What Hit UAE and How
July presented a busy month for novel cybersecurity threats. Public-facing systems were exploited, and sessions were stolen as AI shortened the time between access and damage, while UAE organisations faced pressure on financial services and sustained disruption attempts.
The wider backdrop stayed tense too, with the regional conflict keeping attack volumes across the Gulf elevated. One thread runs through almost all of it, and it is the subject of this month's focus.
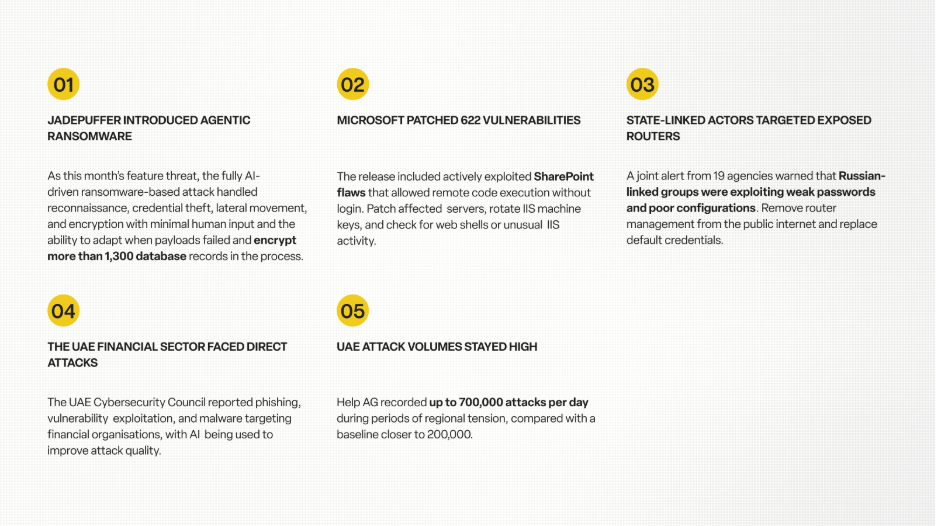
In early July, JadePuffer, the first known ransomware attack that was run end to end by an AI. Handed a foothold in an unpatched, internet-facing AI tool, a language model ran the whole job itself, from reconnaissance to encryption. It fired off more than 600 actions and fixed its own failed login in 31 seconds, with no human steering.
The way in was ordinary. JadePuffer exploited Langflow - a popular AI-app framework building LLM-driven applications and agent workflows - through CVE-2025-3248, a missing-authentication flaw patched over a year earlier that let anyone run code on servers holding cloud and API keys. The shift is speed and reach: what used to need a skilled crew now runs by itself at machine pace, for little more than the price of an AI.
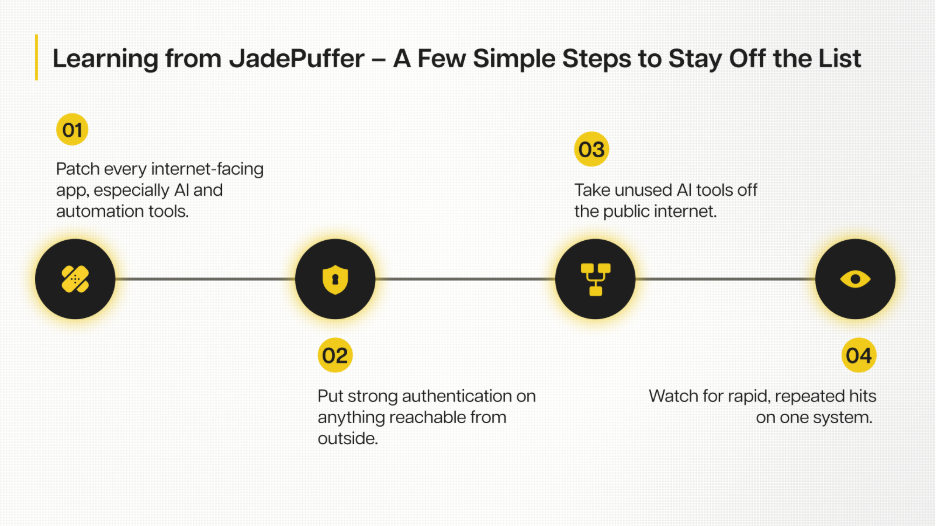
Cybersecurity Thought Of the Month
"Attackers are increasingly using artificial intelligence to develop more advanced techniques." ~ UAE Cyber Security Council
This month gave that warning a face, as AI ran an entire ransomware attack by itself, and the UAE's own financial sector was hit by AI-sharpened campaigns in the same few weeks. What used to need a skilled team is now open to anyone who can simply just rent a model.
The truly uncomfortable part, however, is just how little the defence has changed. JadePuffer walked through a year-old, unpatched hole, and the AI phishing hitting UAE banks still needed someone to click. Speed is the new weapon, which is why breaking old habits matter more.
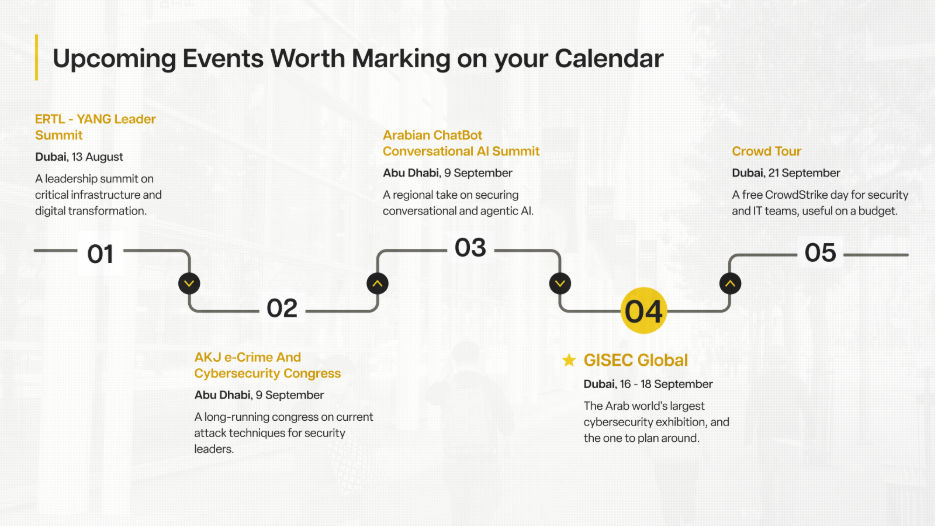
Upcoming Cyber Events in UAE
While July was a lean month in terms of events, the regional circuit reopens in August and builds up to the year's flagship cybersecurity event:
Brought to you by Lumora Security
Thanks for reading till the end.
At Lumora Security, we help SMBs across the UAE find this kind of exposure before an attacker does, whether that is token persistence in a Microsoft 365 tenant or a connected app quietly holding access to your files. Our Essential Security Review maps it in plain language, in a single session, and shows you what to close first.
Never miss an update from The Lumora Security Brief. Subscribe this newsletter on substack or LinkedIn.


